AI evals and guardrails tailored for your business

Get a Demo
Any AI you run
Before launch
Tailored Evals
In production
Runtime Guardrails
Before launch · Tailored Evals
1
Build
You build an AI agent that issues refunds
refunds agent
2
Eval
We generate highly tailored security and safety evals
24 evals
3
Confidence
It goes live only after passing every test
24/24
Pass
In production · Runtime Guardrails
4
Ship
It starts refunding real customers
v1.4
5
Enforce
It tries a $12,400 unauthorized refund. We block it.
$12,400
Blocked
6
Learn
Traces and attack patterns become new evals
eval #25
Every deviation becomes a new eval
Enforcement architecture

Understand data. Know agent blueprint. Enforce at runtime.

Relyance Guard sits between your AI and everything it can reach. Guard generates tailored evals to test before launch. Then in production, every action is checked against what the data is, what the agent may do, and what policies you want enforced.
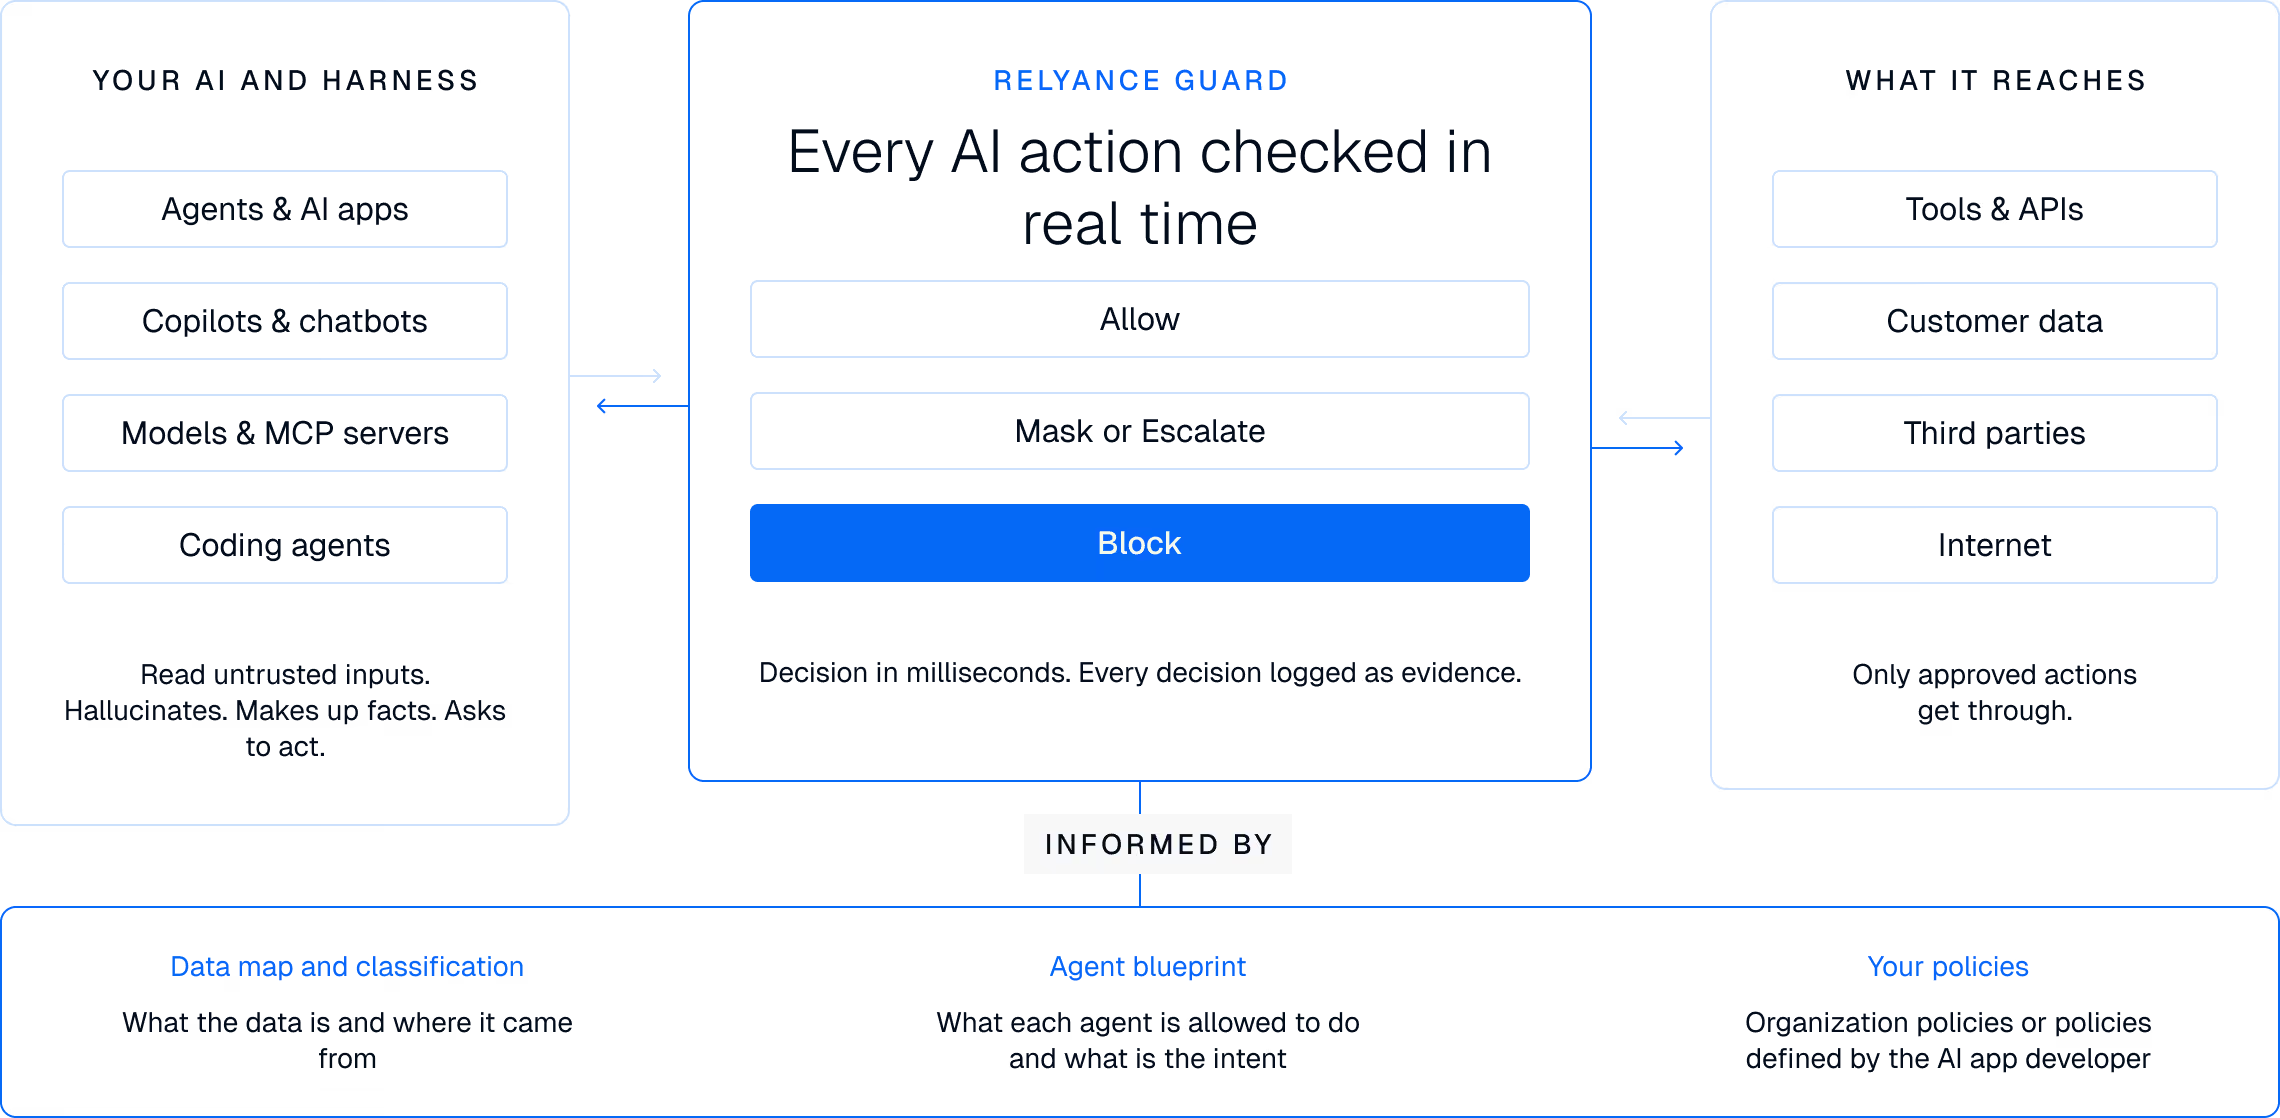
Diagram showing an AI enforcement flow: On the left, 'Your AI and Harness' lists Agents & AI apps, Copilots & chatbots, Models & MCP servers, and Coding agents reading untrusted inputs, hallucinating, and asking to act. In the center, 'Relyance Guard' checks every AI action in real time with options to Allow, Mask or Escalate, or Block, logging decisions as evidence in milliseconds. On the right, 'What It Reaches' includes Tools & APIs, Customer data, Third parties, and Internet, only allowing approved actions through. Below, three sources inform this process: Data map and classification describing data origin, Agent blueprint defining agent actions and intent, and Your policies including organization or developer-defined rules.
Chris Bender
“AI is creating and moving data faster than any team can track. Only AI-native tools like Relyance AI can keep up with the discovery and enforcement loop.”
Chris Bender

CISO
Jason James
“Relyance gives us a complete, contextual understanding of our data landscape. We can see what we have, how it’s used, who owns it, and where the risks are.”
Jason James

CIO
Kathleen Determann
“Within two weeks, we had more insight into our data flows than I ever had in the two years.”
Kathleen Determann

Deputy General Counsel and Chief Compliance and Privacy Officer